
Build Your Pentest
Build each web application, API, mobile application, or infrastructure test separately. Set access level, roles, size, and testing method for each.
Penetration testing
Manual, evidence-based penetration testing for applications, APIs, mobile environments, infrastructure, and cloud, scoped around your technology, risk, and next milestone.
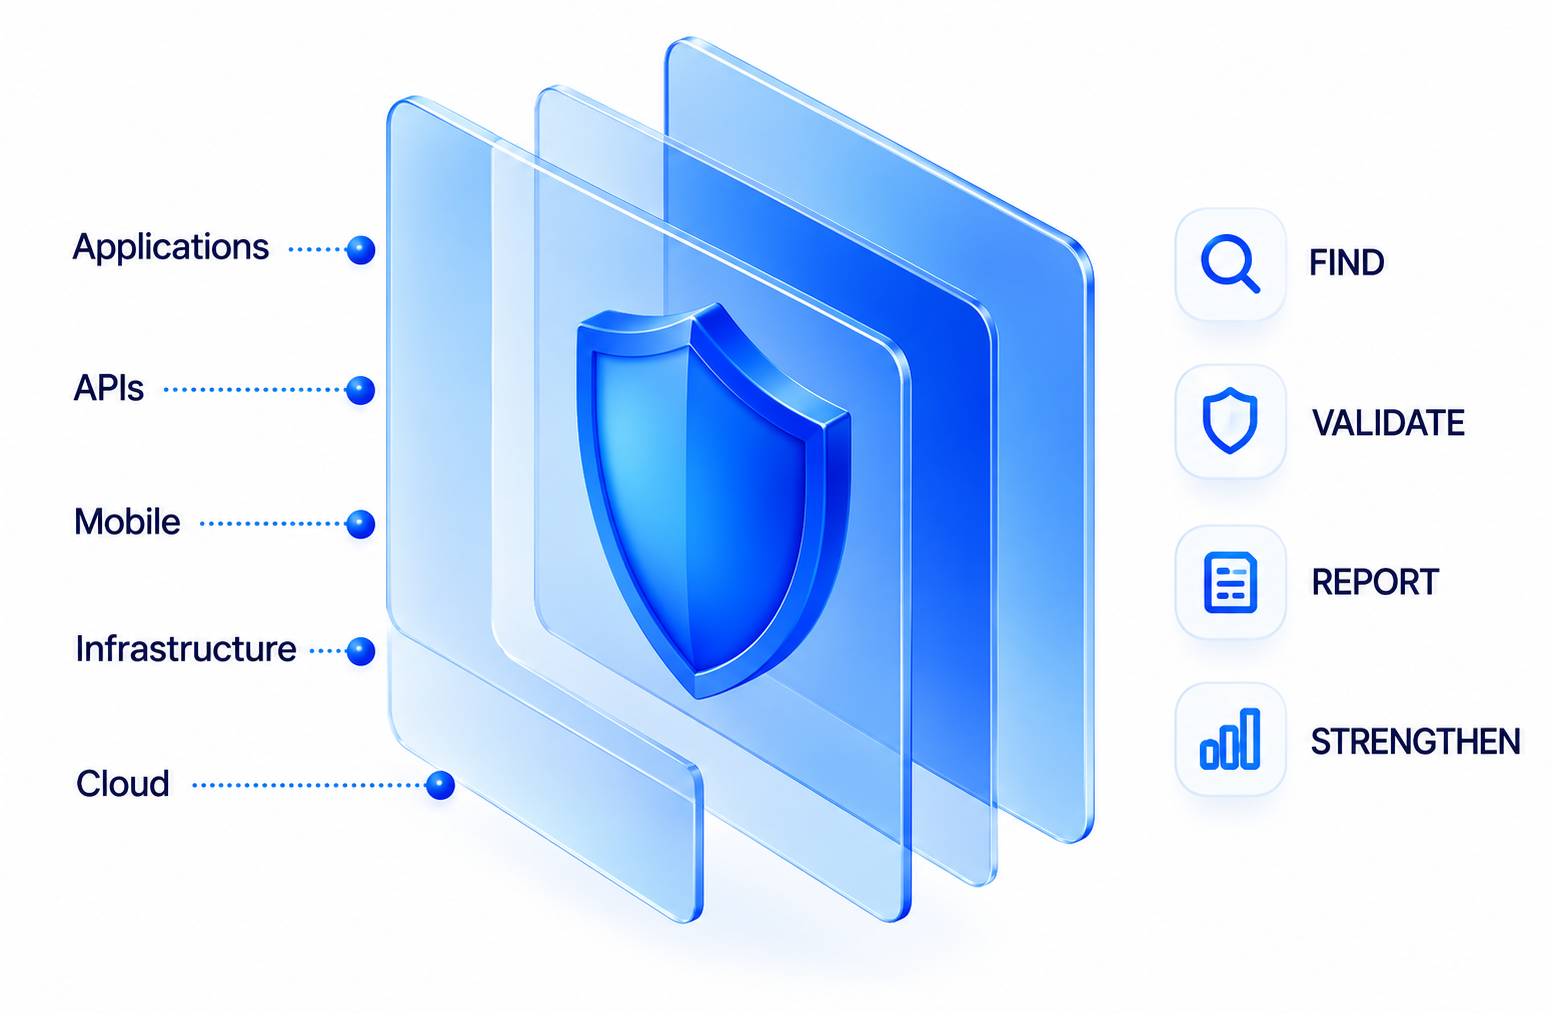
Our coverage
Test the systems that matter without fragmenting scope across multiple vendors.
Black box · Grey box · White box, matched to your environment and testing goals.
Get started
Know exactly what needs testing? Build it test by test. Need guidance? Start with a package and refine it.
Build each web application, API, mobile application, or infrastructure test separately. Set access level, roles, size, and testing method for each.
Start with a plain-English package based on your environment and goal. Review the assumptions, adjust the scope, or switch paths anytime.
Prefer to talk it through? Book a scoping call.
Deliverables
Clear findings, technical context, remediation guidance, and retest validation.
Manual testing and validation against the agreed scope.
Clear findings with evidence and technical context.
Track fixes and verify closure against findings.
Sample output
Penetration Test Report12 findings
Evidence-ready reporting supports remediation, customer diligence, and SOC 2.